
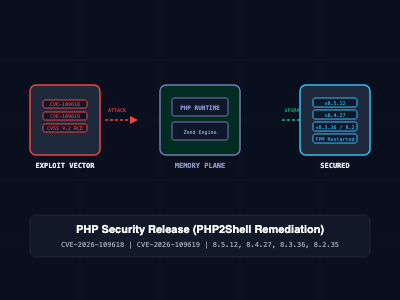
Emergency PHP security updates (8.5.12, 8.4.27, 8.3.36, 8.2.35) fix critical unauthenticated RCE vulnerabilities known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619). Learn root-cause mechanics and run production automated bash/python patching scripts tailored for WordPress, Laravel/Symfony, PHP Native, and Adobe Magento. #PHP #PHP8 #Cybersecurity #WordPress #Laravel #Symfony #Magento #DevOps #AppSec #Linux #SysAdmin #RCE
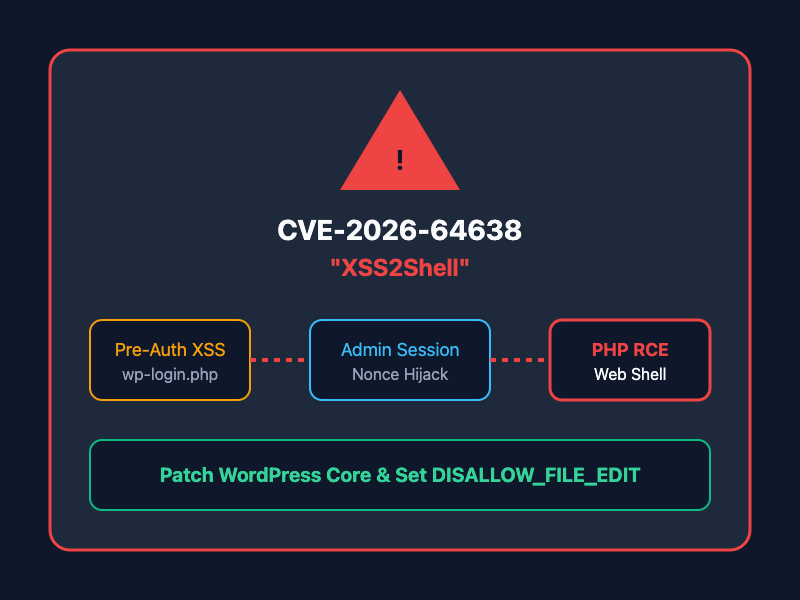
WordPress Core disclosed CVE-2026-64638 (XSS2Shell), a critical pre-authentication reflected XSS on the login screen that escalates to full Remote Code Execution (RCE) when targeting an administrator. Learn how XSS2Shell works under the hood, how the attack chain executes, and how to patch your WordPress infrastructure immediately. #WordPress #Cybersecurity #InfoSec #AppSec #XSS2Shell #CVE202664638 #Vulnerability #DevOps #PHP #WebSecurity