
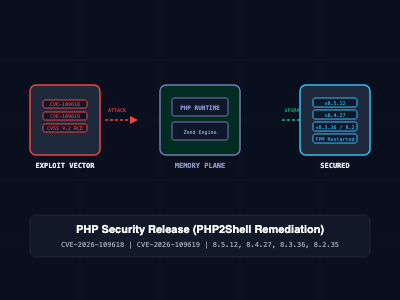
Emergency PHP security updates (8.5.12, 8.4.27, 8.3.36, 8.2.35) fix critical unauthenticated RCE vulnerabilities known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619). Learn root-cause mechanics and run production automated bash/python patching scripts tailored for WordPress, Laravel/Symfony, PHP Native, and Adobe Magento. #PHP #PHP8 #Cybersecurity #WordPress #Laravel #Symfony #Magento #DevOps #AppSec #Linux #SysAdmin #RCE
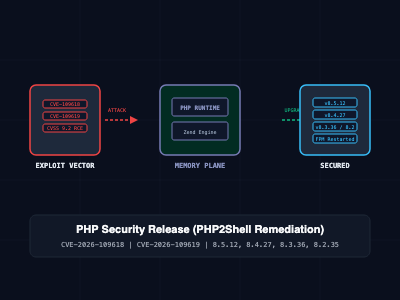
The PHP development team issued emergency security updates for PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35 to remediate two critical unauthenticated Remote Code Execution (RCE) flaws known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619, CVSS 9.2). Learn how OOM corruption and stale global state trigger remote exploitation, audit vulnerable runtimes across PHP-FPM and FrankenPHP, and deploy immediate server patches. #PHP #PHP8 #Cybersecurity #DevOps #AppSec #Infosec #Linux #SysAdmin #Laravel #RCE
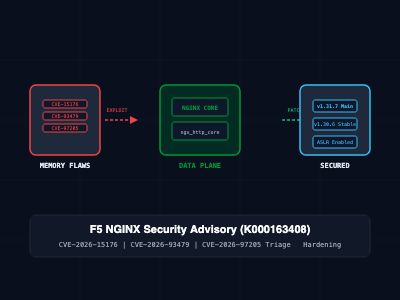
F5 released emergency security updates for NGINX Open Source and NGINX Plus addressing three high-severity memory corruption flaws: CVE-2026-15176 (heap buffer overflow via alias rewrite), CVE-2026-93479 (heap overflow via map regex captures), and CVE-2026-97205 (use-after-free via AIO and SSI). Learn how to audit vulnerable directives, configure immediate mitigations, and patch production ingress controllers. #NGINX #F5 #Cybersecurity #Infosec #DevOps #SRE #AppSec #DevSecOps #Linux #SysAdmin
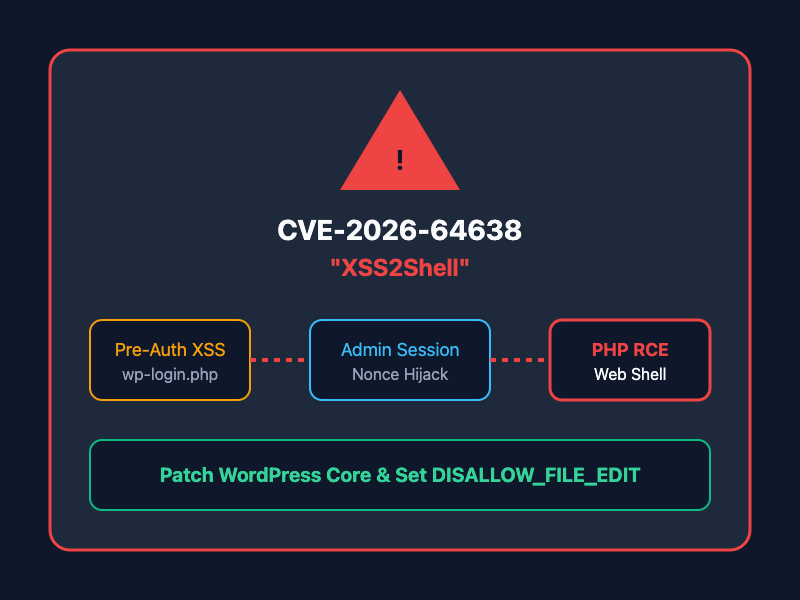
WordPress Core disclosed CVE-2026-64638 (XSS2Shell), a critical pre-authentication reflected XSS on the login screen that escalates to full Remote Code Execution (RCE) when targeting an administrator. Learn how XSS2Shell works under the hood, how the attack chain executes, and how to patch your WordPress infrastructure immediately. #WordPress #Cybersecurity #InfoSec #AppSec #XSS2Shell #CVE202664638 #Vulnerability #DevOps #PHP #WebSecurity
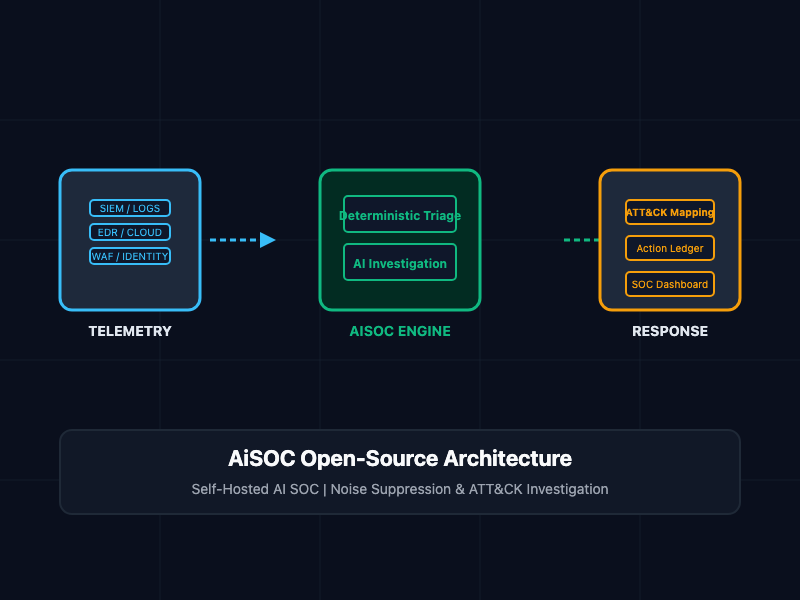
Alert fatigue and manual triage bottlenecks severely stall security response teams. AiSOC solves this by delivering an open-source, self-hostable AI Security Operations Center powered by agentic alert fusion, automated MITRE ATT&CK investigation ledgers, and deterministic triage engines. Learn how to deploy AiSOC to reduce alert noise and automate incident response. #AiSOC #SOC #Cybersecurity #DevSecOps #OpenSource #AIEngineering #MITREATTACK #ThreatIntelligence #Infosec #SecurityAutomation
The Node.js project has announced critical security releases for the 26.x, 24.x, and 22.x release lines, addressing high-severity vulnerabilities across supported LTS and current distributions. This technical guide breaks down the release scope, potential risks for EOL environments, and actionable patch management strategies to protect your backend infrastructure. #Nodejs #SecurityRelease #Cybersecurity #BackendDevelopment #PatchManagement #Node26 #Node24 #Node22 #DevSecOps #Infosec
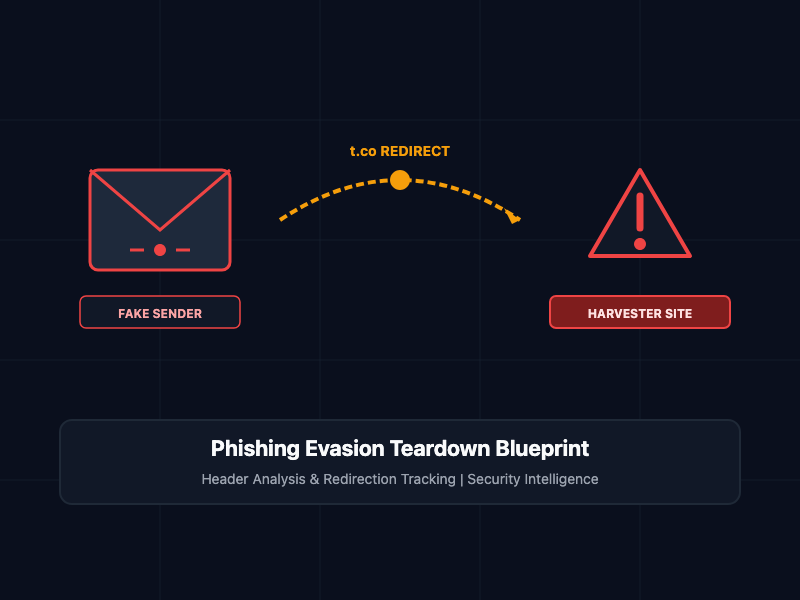
Social engineers continuously exploit high-trust consumer brands like Netflix to execute urgent credential harvesting campaigns. This technical analysis deconstructs a live phishing artifact that combines sender address spoofing with Twitter (t.co) redirect bypasses to evade Secure Email Gateways (SEGs). #Phishing #Cybersecurity #ThreatIntelligence #EmailSecurity #Infosec #SecOps #SocialEngineering #Ransomware #BlueTeam
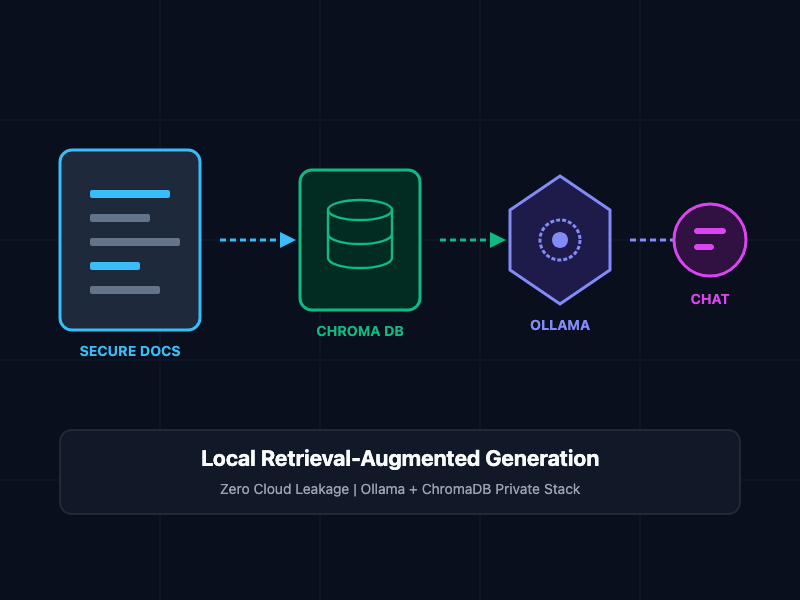
Introduces severe data privacy and intellectual property risks. This technical guide explains how to construct a fully local, secure, and cost-effective Retrieval-Augmented Generation (RAG) pipeline. Learn how to parse local documents, generate vector embeddings, and interact with your data privately using Ollama, Python, and ChromaDB. #LocalLLM #Ollama #RAG #ChromaDB #Python #GenerativeAI #DataPrivacy #DataSecurity #VectorDatabase #AI

A critical Remote Code Execution (RCE) vulnerability affecting Ivanti Endpoint Manager Mobile (EPMM), to its Known Exploited Vulnerabilities (KEV) catalog. This technical guide analyzes the exploit vector, details immediate detection commands, and provides actionable remediation steps to secure your mobile device management infrastructure. #CVE20266973 #Ivanti #EPMM #MobileIron #RemoteCodeExecution #CISA #KEV #VulnerabilityManagement #ThreatIntelligence #Cybersecurity #SecOps #NetworkSecurity

Many organizations confuse vulnerability scanning with penetration testing, leading to misallocated budgets and dangerous security blind spots. This guide breaks down the core differences, technical workflows, and operational use cases of both methods to help you build a robust, compliant defense posture. #Cybersecurity #Infosec #VulnerabilityScanning #PenetrationTesting #DevSecOps #AppSec #SecOps #Compliance #RiskManagement #SecurityAuditing #NetworkSecurity #EthicalHacking