
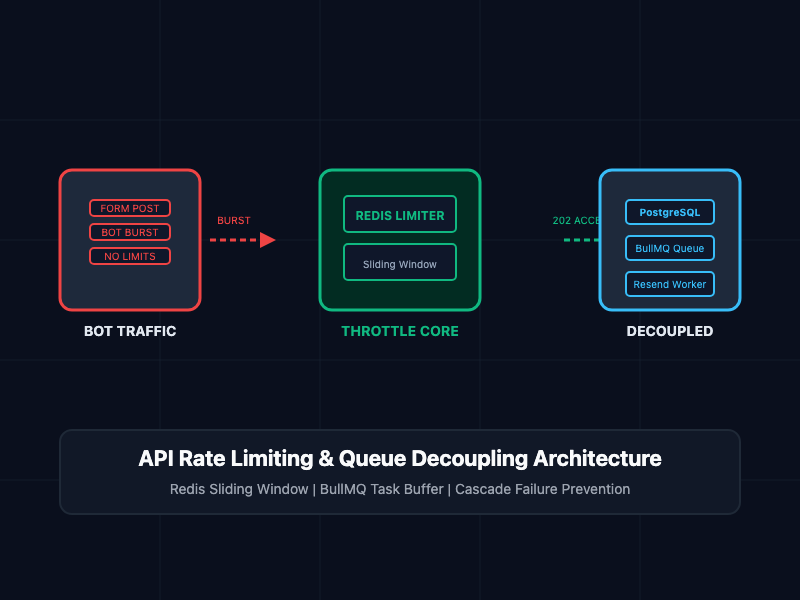
A simple newsletter subscription form without API rate limiting triggered a cascading production outage on a logistics platform. Unthrottled requests caused database connection exhaustion, depleted third-party email quotas on Resend, and generated costly infrastructure bills. Learn how to implement Redis-backed sliding window rate limiting, decouple email dispatch with message queues & bot. #RateLimiting #SystemDesign #DevOps #SRE #Nodejs #Redis #Cybersecurity #WebSecurity #BackendDevelopment
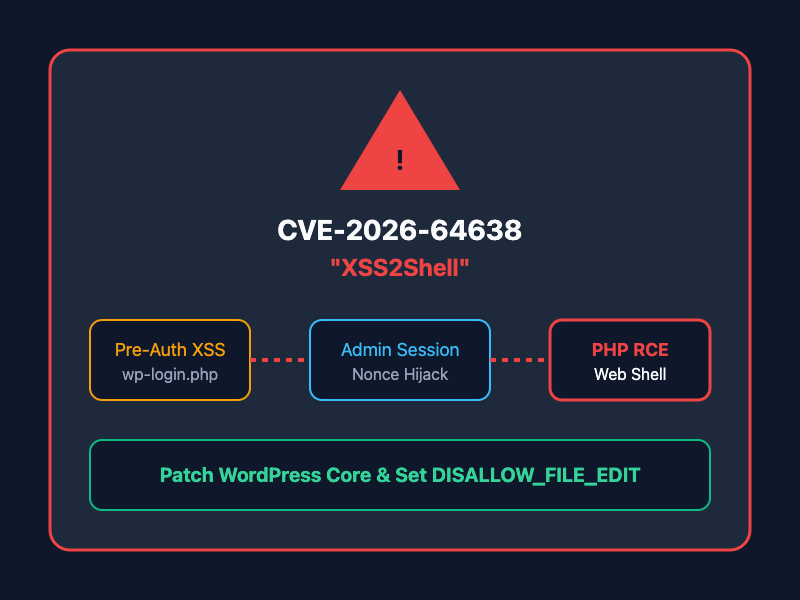
WordPress Core disclosed CVE-2026-64638 (XSS2Shell), a critical pre-authentication reflected XSS on the login screen that escalates to full Remote Code Execution (RCE) when targeting an administrator. Learn how XSS2Shell works under the hood, how the attack chain executes, and how to patch your WordPress infrastructure immediately. #WordPress #Cybersecurity #InfoSec #AppSec #XSS2Shell #CVE202664638 #Vulnerability #DevOps #PHP #WebSecurity