
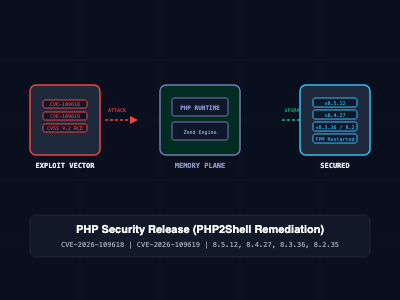
Emergency PHP security updates (8.5.12, 8.4.27, 8.3.36, 8.2.35) fix critical unauthenticated RCE vulnerabilities known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619). Learn root-cause mechanics and run production automated bash/python patching scripts tailored for WordPress, Laravel/Symfony, PHP Native, and Adobe Magento. #PHP #PHP8 #Cybersecurity #WordPress #Laravel #Symfony #Magento #DevOps #AppSec #Linux #SysAdmin #RCE
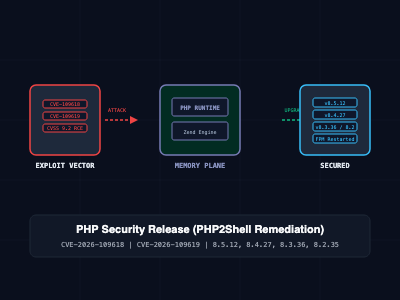
The PHP development team issued emergency security updates for PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35 to remediate two critical unauthenticated Remote Code Execution (RCE) flaws known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619, CVSS 9.2). Learn how OOM corruption and stale global state trigger remote exploitation, audit vulnerable runtimes across PHP-FPM and FrankenPHP, and deploy immediate server patches. #PHP #PHP8 #Cybersecurity #DevOps #AppSec #Infosec #Linux #SysAdmin #Laravel #RCE
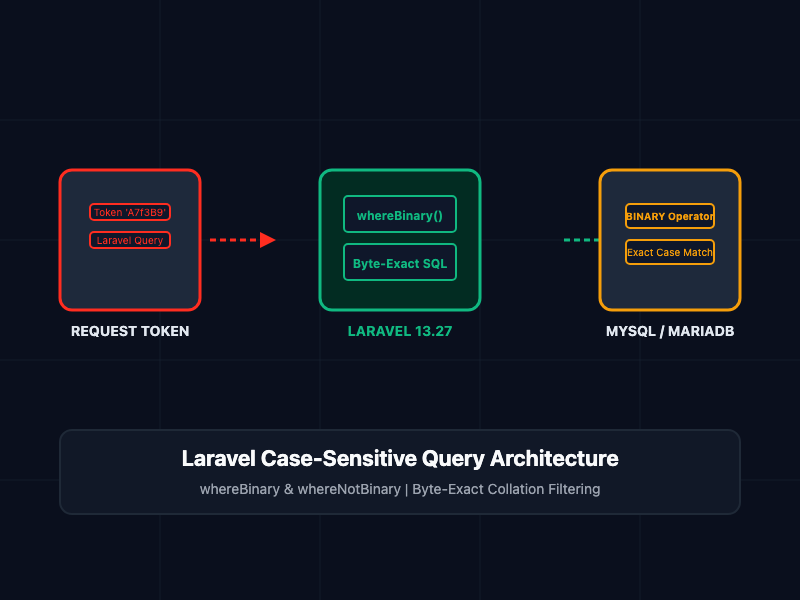
Default MySQL collations compare strings case-insensitively, matching tokens like 'A7f3B9' and 'a7f3b9'. Laravel 13.27 introduces whereBinary() and whereNotBinary() for byte-exact, case-sensitive database queries natively in Eloquent. Learn how to optimize query indexing and prevent collation bugs. #Laravel #PHP #MySQL #Database #Eloquent #Backend #SQL #WebDev #LaravelDev #DatabaseDesign
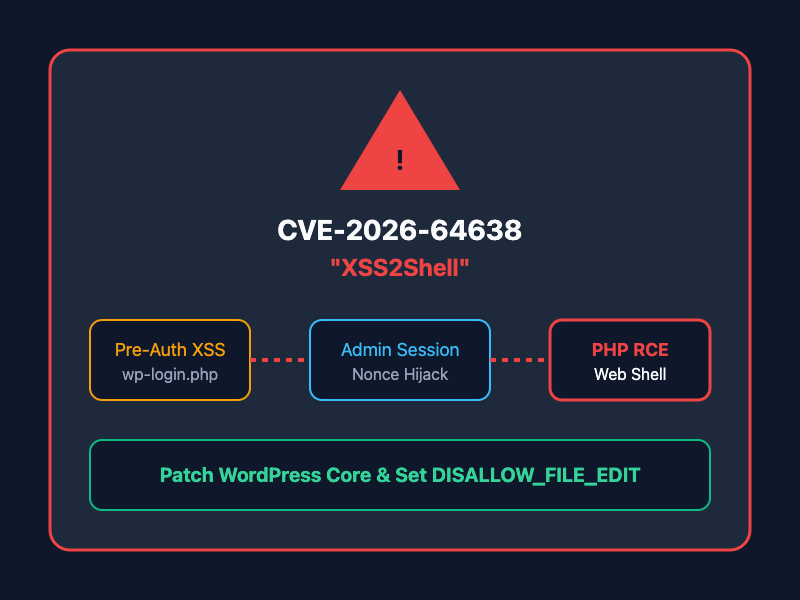
WordPress Core disclosed CVE-2026-64638 (XSS2Shell), a critical pre-authentication reflected XSS on the login screen that escalates to full Remote Code Execution (RCE) when targeting an administrator. Learn how XSS2Shell works under the hood, how the attack chain executes, and how to patch your WordPress infrastructure immediately. #WordPress #Cybersecurity #InfoSec #AppSec #XSS2Shell #CVE202664638 #Vulnerability #DevOps #PHP #WebSecurity
Learn how to seamlessly integrate Laravel and React to build scalable, full-stack web applications. This complete guide covers setting up robust RESTful APIs with Laravel, building dynamic front-end user interfaces with React, state management, and modern development best practices. #Laravel #ReactJS #FullStack #WebDevelopment #PHP #JavaScript #APIDevelopment #TechBlog